EU AI Act Article 9: Risk management system

Providers of high-risk AI systems need a documented risk management system, kept up to date for the system’s whole life.

Does this apply to me?

  • YesHigh-risk system provider Art. 16
  • DependsDeployer, importer, distributor, if you become the provider Art. 25(1)
  • NoSystem that is not high-risk Art. 9(1)

By when?

  1. 2 Dec 2027Annex III systems

    398 days left, nextArt. 113(c)(i), as amended

  2. 2 Aug 2028Annex I systems

    642 days left, laterArt. 113(c)(ii), as amended

Applies 2 Dec 2027Maximum fine €15M or 3% Art. 99(4), point (a), through the provider obligations in Art. 164 min readPlain-words summary. The quoted text below is the law.

Reviewed by Ajay Pundhir, founder

This page does not tell you whether your system is high-risk. Article 6 and Annex III decide that.

How it works

The risk management loop

  1. Step 1: IdentifyFind and analyse the known and reasonably foreseeable risks to health, safety or fundamental rights.Art. 9(2)(a)
  2. Step 2: EvaluateEstimate and evaluate the risks under intended use and under reasonably foreseeable misuse.Art. 9(2)(b)
  3. Step 3: MitigateAdopt appropriate and targeted measures for the risks you identified.Art. 9(2)(d)
  4. Step 4: TestTest to find the most appropriate measures and to show the system performs consistently for its intended purpose.Art. 9(6)

Back to step 1. Repeat for the whole lifecycle, with regular systematic review and updating. Art. 9(2)

The steps quoted on this page, in one pass. Article 9 has more; read it in full on EUR-Lex.

Roles

Who does what

Provider

  • Establish, implement, document and maintain the risk management system. Art. 9(1)
  • Run it for the whole lifecycle and review it regularly. Art. 9(2)

Deployer

  • No Article 9 duty unless you become the provider. Art. 25(1)

Importer

  • No Article 9 duty unless you become the provider. Art. 25(1)

Distributor

  • No Article 9 duty unless you become the provider. Art. 25(1)

Checklist

What to do

Ticks stay on this page only. Nothing is saved.

  1. Art. 9(1)Show the law for this row (Art. 9(1))

  2. Art. 9(2)Show the law for this row (Art. 9(2))

    Worked example: A credit-scoring model, retrained

    Example

    A credit-scoring model, retrained

    A provider retrains its creditworthiness model on new data six months after release.

    Outcome
    The risk management system is reviewed and updated for the new version. The first assessment does not carry over unchanged.
    Why
    Paragraph 2 calls the system a continuous iterative process that needs regular systematic review and updating. Art. 9(2)
  3. Art. 9(2)(a)Show the law for this row (Art. 9(2)(a))

    Worked example: A CV-screening model

    Example

    A CV-screening model

    A company sells a model that ranks job applicants for employers in the EU.

    Outcome
    If the model is high-risk under Article 6 and Annex III, the company is its provider and needs the risk management system.
    Why
    Annex III lists employment uses, and Article 9 applies to high-risk AI systems. Art. 9(1)Annex III
  4. Art. 9(2)(b)Show the law for this row (Art. 9(2)(b))

    Worked example: A score used on its own

    Example

    A score used on its own

    The same company tells customers the score is one input for a human reviewer. A customer could still reject applicants on the score alone.

    Outcome
    If that use is reasonably foreseeable, the risk evaluation covers it too, not only the intended use.
    Why
    Point (b) asks for evaluation under intended use and under conditions of reasonably foreseeable misuse. Art. 9(2)(b)
  5. Art. 9(2)(d)Show the law for this row (Art. 9(2)(d))

  6. Art. 9(6)Show the law for this row (Art. 9(6))

Fictional scenarios

Worked examples

Example

A CV-screening model

A company sells a model that ranks job applicants for employers in the EU.

Outcome
If the model is high-risk under Article 6 and Annex III, the company is its provider and needs the risk management system.
Why
Annex III lists employment uses, and Article 9 applies to high-risk AI systems. Art. 9(1)Annex III

Example

A score used on its own

The same company tells customers the score is one input for a human reviewer. A customer could still reject applicants on the score alone.

Outcome
If that use is reasonably foreseeable, the risk evaluation covers it too, not only the intended use.
Why
Point (b) asks for evaluation under intended use and under conditions of reasonably foreseeable misuse. Art. 9(2)(b)

Example

A credit-scoring model, retrained

A provider retrains its creditworthiness model on new data six months after release.

Outcome
The risk management system is reviewed and updated for the new version. The first assessment does not carry over unchanged.
Why
Paragraph 2 calls the system a continuous iterative process that needs regular systematic review and updating. Art. 9(2)

Read the text

Common mistakes

  • Common mistake

    Treating it as a one-off assessment before launch.

    What the text says

    “a continuous iterative process planned and run throughout the entire lifecycle” Art. 9(2)

  • Common mistake

    Assessing only the intended use.

    What the text says

    “used in accordance with its intended purpose, and under conditions of reasonably foreseeable misuse” Art. 9(2)(b)

  • Common mistake

    Listing risks without deciding what to do about them.

    What the text says

    “the adoption of appropriate and targeted risk management measures” Art. 9(2)(d)

  • Common mistake

    Keeping the process in people’s heads.

    What the text says

    “established, implemented, documented and maintained” Art. 9(1)

Regulation (EU) 2026/1744 · in force 27 Jul 2026

What changed

High-risk dates move to 2 Dec 2027 (Annex III) and 2 Aug 2028 (Annex I)

Change in lawArticle 113, third paragraph, point (c)
It shall apply from 2 August 2026.
Removed: (c) Article 6(1) and the corresponding obligations in this Regulation shall apply from 2 August 2027.Added: (c) Chapter III, Sections 1, 2, and 3, with the exception of Article 6(5), shall apply from:Added: (i) 2 December 2027 as regards AI systems classified as high-risk pursuant to Article 6(2) and Annex III; andAdded: (ii) 2 August 2028 as regards AI systems classified as high-risk pursuant to Article 6(1) and Annex I;

The context line is the second paragraph of Article 113, which set the date for Annex III systems before the change. Removed and context lines quote Regulation (EU) 2024/1689 as adopted; added lines quote the amending Regulation.

Source: Regulation (EU) 2026/1744, Article 1, point (40), verified 4 Oct 2026

Quoted from EUR-Lex

What Article 9 says

The quoted text of Article 9 (6 paragraphs)
9(1)

1. A risk management system shall be established, implemented, documented and maintained in relation to high-risk AI systems.

9(2)

2. The risk management system shall be understood as a continuous iterative process planned and run throughout the entire lifecycle of a high-risk AI system, requiring regular systematic review and updating. It shall comprise the following steps:

9(2)(a)

(a) the identification and analysis of the known and the reasonably foreseeable risks that the high-risk AI system can pose to health, safety or fundamental rights when the high-risk AI system is used in accordance with its intended purpose;

9(2)(b)

(b) the estimation and evaluation of the risks that may emerge when the high-risk AI system is used in accordance with its intended purpose, and under conditions of reasonably foreseeable misuse;

9(2)(d)

(d) the adoption of appropriate and targeted risk management measures designed to address the risks identified pursuant to point (a).

9(6)

6. High-risk AI systems shall be tested for the purpose of identifying the most appropriate and targeted risk management measures. Testing shall ensure that high-risk AI systems perform consistently for their intended purpose and that they are in compliance with the requirements set out in this Section.

Selected paragraphs, quoted exactly. Read the whole article in Regulation (EU) 2024/1689 on EUR-Lex. Checked 4 Oct 2026.

Coverage: Covered

RiskForge

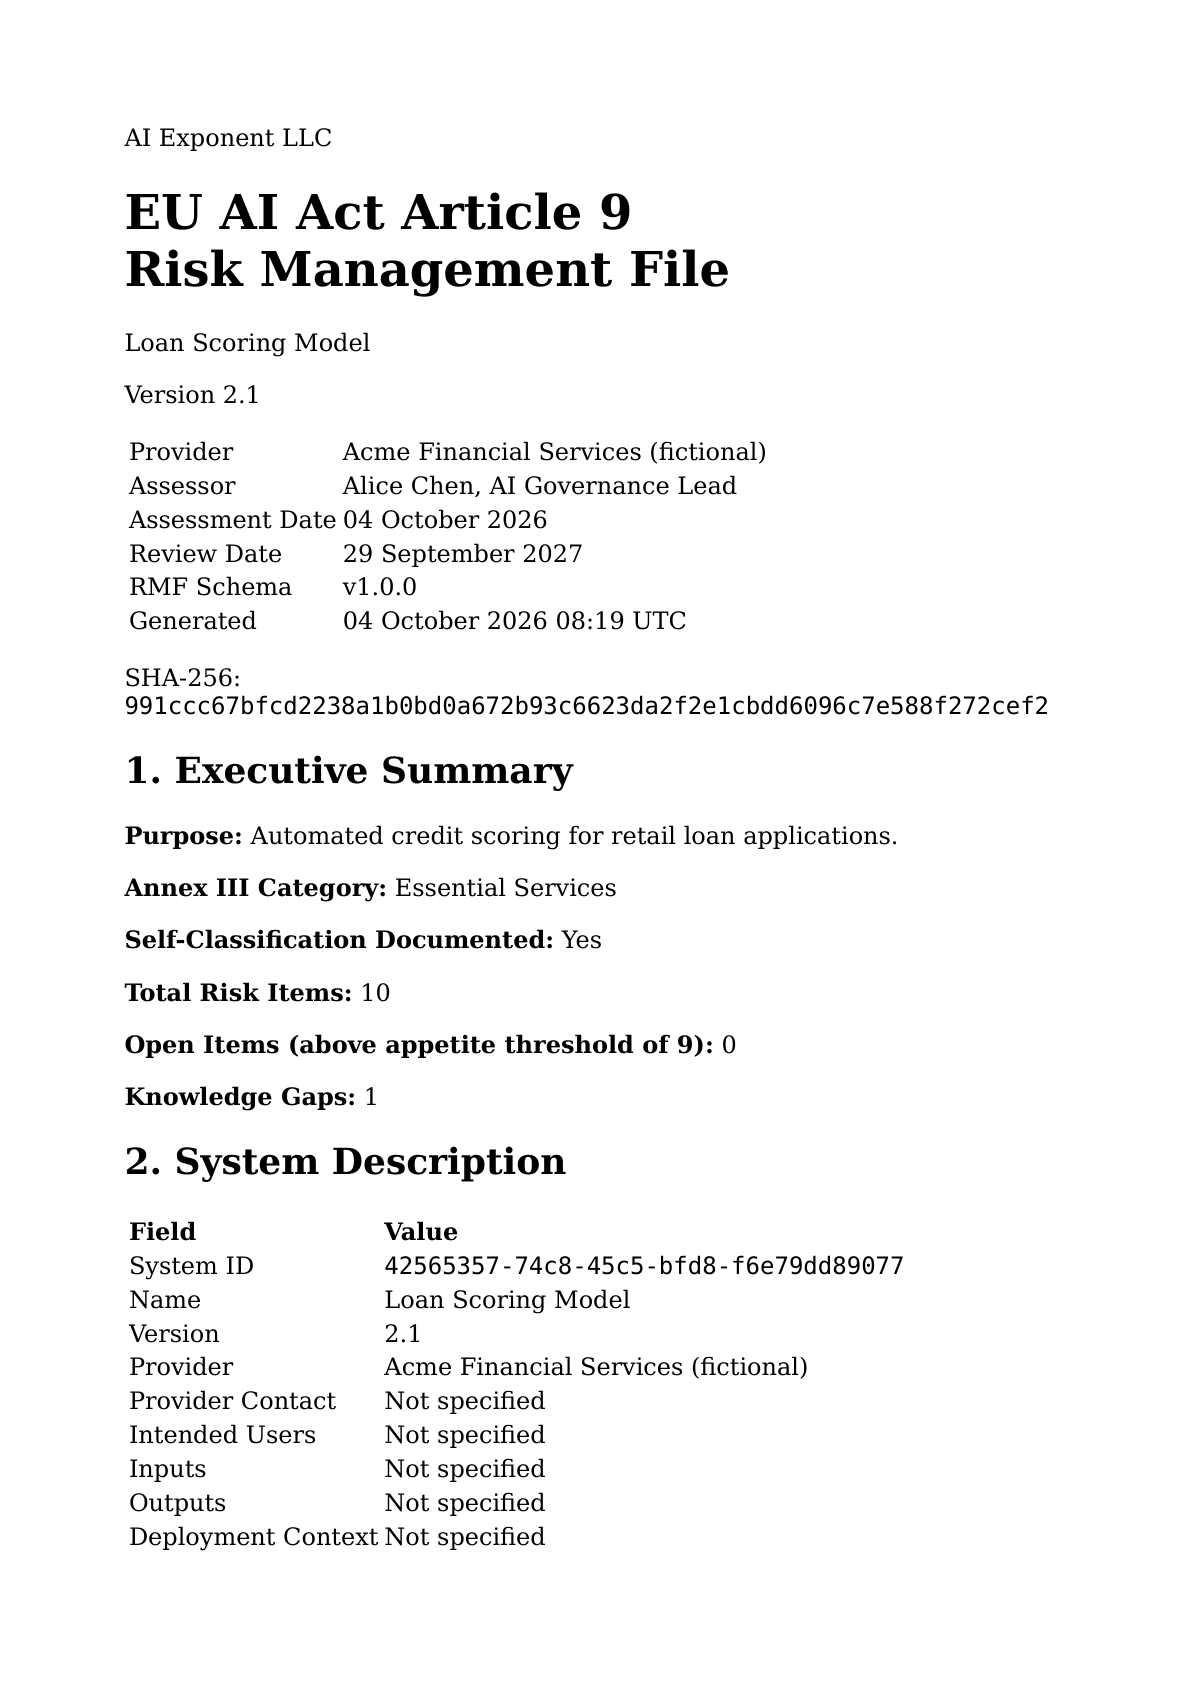
RiskForge produces a Risk Management File in JSON for your Annex IV technical documentation pack. It covers eight risk dimensions with 37 questions, logs each assessment change, and cross-maps to NIST AI RMF and ISO/IEC 42001. You run the assessment in a terminal, or from a YAML answers file in scripts and CI. RiskForge is a screening and documentation artefact, not a substitute for notified-body conformity assessment.

From the fact register

Questions about Article 9

When does Article 9 apply?
It applies from 2 Dec 2027 for high-risk systems listed in Annex III (Art. 113(c)(i), as amended), and from 2 Aug 2028 for high-risk systems covered by Annex I (Art. 113(c)(ii), as amended). Before Regulation (EU) 2026/1744, the dates were 2 Aug 2026 and 2 Aug 2027.
What is the maximum fine for breaching Article 9?
Up to €15 million or 3% of total worldwide annual turnover for the preceding financial year, whichever is higher (Art. 99(4), point (a), through the provider obligations in Art. 16). For SMEs, including start-ups, the fine is capped at whichever of the two is lower (Art. 99(6)). Since 27 Jul 2026, the same lower cap applies to small mid-cap enterprises (Art. 99(6a)).
Did the Digital Omnibus change Article 9?
Its text is unchanged. Regulation (EU) 2026/1744 moved the date it applies from, through Article 113. The section "What changed" quotes the old and new text.
Is there an AiExponent tool for Article 9?
Yes. RiskForge is released and open source. It writes a Risk Management File (JSON / PDF).

On askajay.ai

Further reading

Content verified 26 Oct 2026 · Not legal advice.